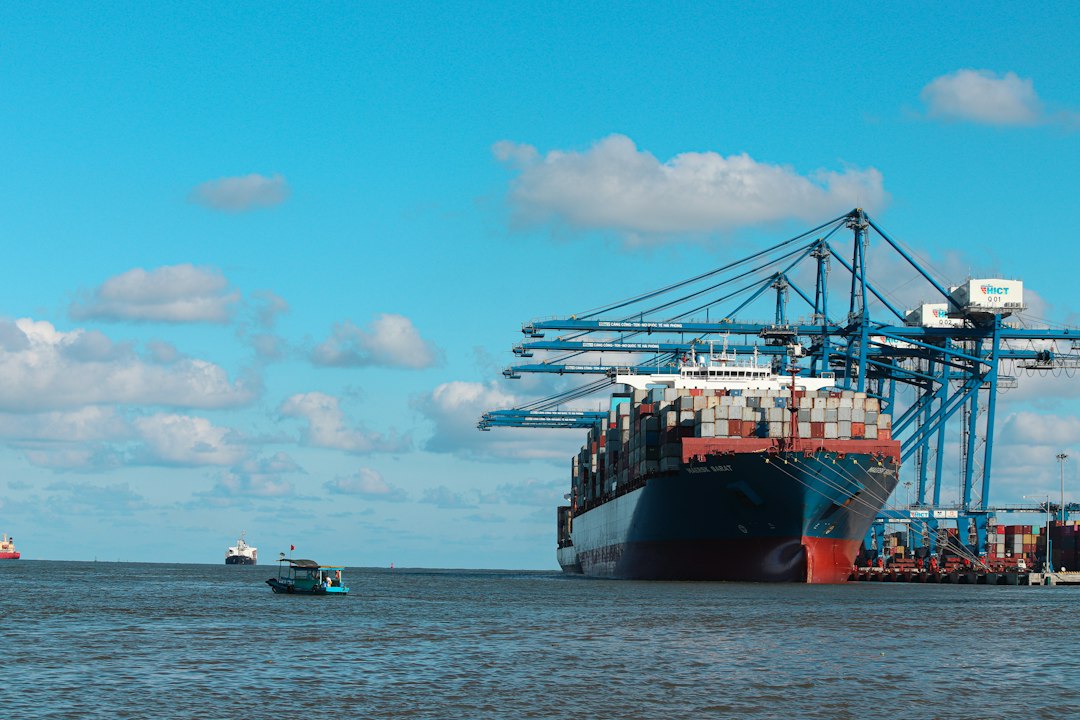
On October 27, 2026, industry leaders announced the launch of the first public database specifically focused on cyber vulnerabilities that impact the maritime sector. Named the Blue Initiative, this collaboration includes Cydome, ClassNK, Bureau Veritas, MTS-ISAC, and Rakuten Maritime. Accessible at blue-initiative.org, the initiative aims to equip shipping companies with vital tools to identify and mitigate risks associated with their IT and operational technology (OT) devices.
The Need for a Dedicated Database
The alarming increase in cybersecurity threats has underscored the need for specialized resources within the maritime industry. With over 350,000 published Common Vulnerabilities and Exposures (CVEs) and around 200 new entries emerging daily, the task of prioritizing relevant system patches has become increasingly complex for maritime operators. Cydome’s CEO, Nir Ayalon, emphasized the challenges posed by the sheer volume of cybersecurity information and the necessity for a focused approach tailored to maritime systems.
Collaboration and Contributions
The Blue Initiative signifies a concerted effort among key players in the maritime sector to streamline cybersecurity practices. ClassNK, Bureau Veritas, and others recognize the importance of a shared reference point for identifying vulnerabilities pertinent to maritime IT and OT equipment. As Panagiotis Anastasiou from Bureau Veritas highlighted, having a specific database can alleviate the difficulties faced in decoding general information scattered across various platforms. This collective effort not only enhances individual company cybersecurity posture but also elevates the entire maritime industry’s resilience against cyber threats.
Operational Implications
The introduction of the Blue Initiative is particularly timely due to the evolving technological landscape, which is increasingly exploited by cybercriminals. The MTS-ISAC’s endorsement of this collaborative model reflects a growing recognition of the need for well-coordinated vulnerability management strategies applicable throughout a vessel’s operational lifecycle. Continuous updates and a community-driven approach to data validation can empower shipping companies to act swiftly against emerging vulnerabilities, thereby fortifying their critical infrastructure.
Why It Matters
The launch of the Blue Initiative marks a significant advancement in maritime cybersecurity through a concentrated focus on vulnerabilities relevant to the industry. For operators, this collaborative database is not merely a tool but a necessity for effective risk management. As vulnerabilities proliferate, the challenge of prioritizing responses escalates; thus, having a tailored resource can streamline these efforts significantly. Companies are encouraged to engage with this initiative, ensuring that the data remains relevant and actionable. As cybersecurity remains a critical concern, the industry must adapt and respond swiftly to new threats while maintaining operational readiness.